Connect Microsoft Foundry to import its models into the Model Catalogue and its agents into the Agent Catalogue. Using Azure OpenAI Service, Azure AI Services (Classic), Azure Machine Learning or Foundry Agent Service (Classic)? See Microsoft Foundry (classic) Integration.
Saidot reads your Foundry resource through Saidot's own service principal. You link your tenant to Saidot, then give that service principal read-only access to the Foundry resource.
Before you start you need:
-
Your Azure tenant ID
-
Either the Azure resource ID of the Foundry resource, or the Foundry project endpoint URL, subscription ID and resource group (step 3 shows where to find them)
-
Rights to create custom roles and assign roles on the Foundry resource (for example Owner, or User Access Administrator)
Step 1. Connect your tenant
Enter your Azure tenant ID and approve the consent prompt. This links Saidot's tenant to yours, so the Saidot service principal appears in your Microsoft Entra ID and you can assign it a role in step 2.
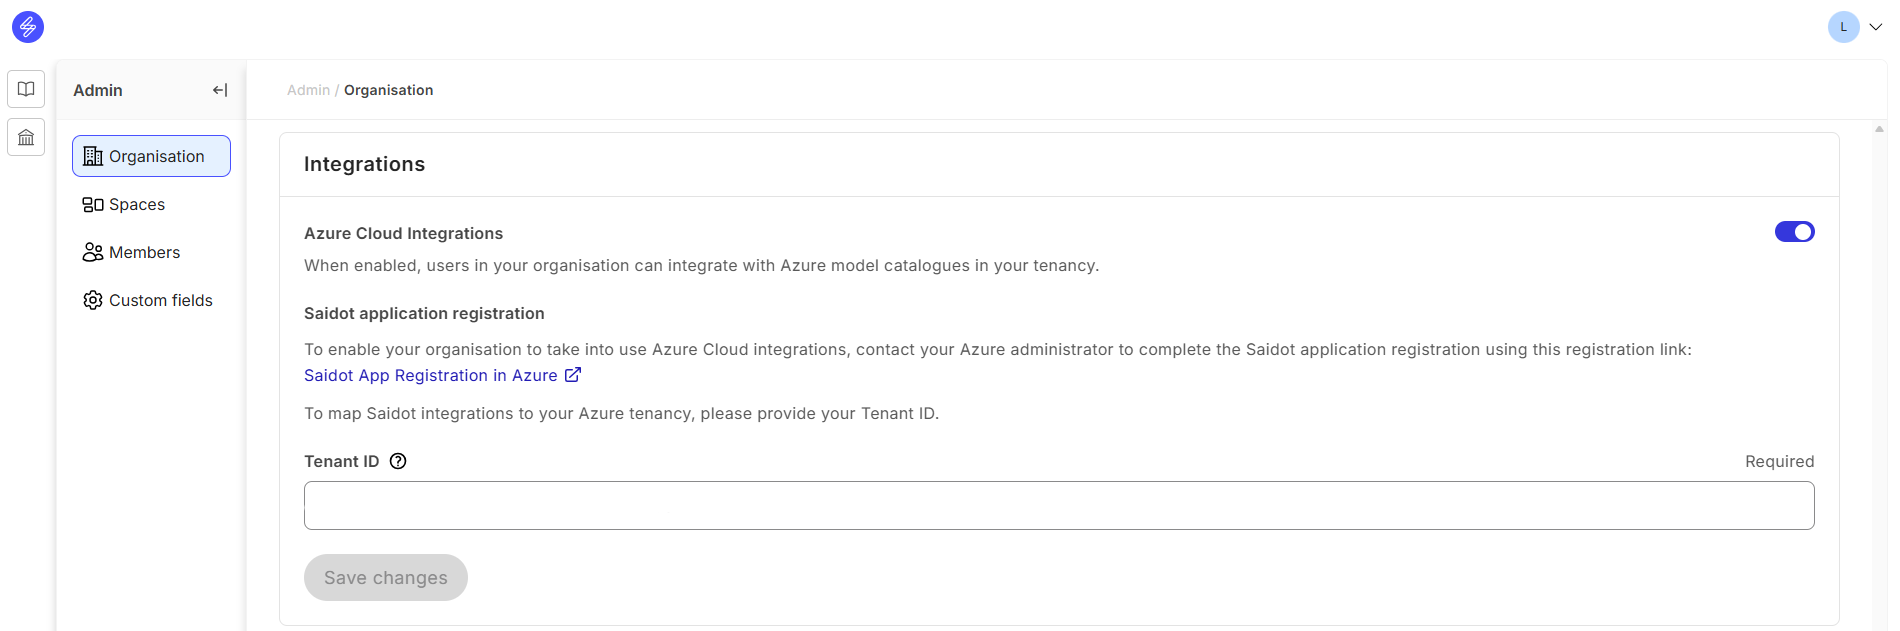
Step 2. Give Saidot read access to the Foundry resource
The built-in Reader role is not enough: it does not let Saidot read agents. No built-in role is read-only for agents. The built-in roles that can read agents (for example Foundry User, formerly Azure AI User, or Cognitive Services User) also allow creating, changing and deleting agents and calling models. Choose one of these two options.
|
|
Option A: Custom role (recommended) |
Option B: Foundry User |
|---|---|---|
|
What Saidot can do |
Read models, deployments and agents only |
Read everything, and also create, run and change agents and deployments |
|
Privilege |
Least privilege, read-only |
Broad data-plane access |
|
Setup effort |
Create a custom role once, then assign it |
Assign a built-in role |
|
Choose it when |
You want Saidot to have inventory access only |
Your organization cannot create custom roles, and you accept the wider access |
Option A. Create and assign a custom role (recommended)
The custom role Saidot Microsoft Foundry Inventory Reader keeps Saidot's access read-only:
|
Permission |
Type |
What it allows Saidot to do |
|---|---|---|
|
|
Action |
Read the Foundry resource, projects, models and deployments |
|
|
Data action |
Read agents in your projects |
Assign the role on the Foundry resource, not on a project. The role then applies to every project in that resource, so agents in all projects are covered. If you assign it only on a project, Saidot cannot read the models on the resource.
Create the role
-
In the Azure Portal, open the resource group that holds the Foundry resource.
-
Go to Access control (IAM) → Add → Add custom role.
-
Open the JSON tab, select Edit and paste the definition below. Replace
<subscription-id>and<resource-group>. -
Select Review + create → Create.
{
  "properties": {
    "roleName": "Saidot Microsoft Foundry Inventory Reader",
    "description": "Read-only access for Saidot to Microsoft Foundry resources, models, deployments and agents.",
    "assignableScopes": [
      "/subscriptions/<subscription-id>/resourceGroups/<resource-group>"
    ],
    "permissions": [
      {
        "actions": [
          "Microsoft.CognitiveServices/*/read"
        ],
        "notActions": [],
        "dataActions": [
          "Microsoft.CognitiveServices/accounts/AIServices/agents/read"
        ],
        "notDataActions": []
      }
    ]
  }
}
Assign the role
-
Open the Foundry resource in the Azure Portal.
-
Go to Access control (IAM) → Add → Add role assignment.
-
On the Role tab, search for Saidot Microsoft Foundry Inventory Reader (custom roles are listed under Job function roles).
-
On the Members tab, choose User, group, or service principal, select Select members and search for (Saidot application name – to add).
-
Select Review + assign.
Or use the Azure CLI
Save the JSON above as saidot-role.json, then run:
az role definition create --role-definition saidot-role.json
az role assignment create \
  --assignee <saidot-service-principal-object-id> \
  --role "Saidot Microsoft Foundry Inventory Reader" \
  --scope /subscriptions/<subscription-id>/resourceGroups/<resource-group>/providers/Microsoft.CognitiveServices/accounts/<foundry-resource-name>
A new role assignment can take a few minutes to take effect.
Microsoft guides: Create or update Azure custom roles using the Azure portal · Assign Azure roles using the Azure portal
Option B. Assign the Foundry User role
Warning: Foundry User (formerly Azure AI User) gives broad data-plane access, including creating and running agents and deployments. That is far more than Saidot needs to list your models and agents. Use it only if you accept that access.
-
Open the Foundry resource in the Azure Portal.
-
Go to Access control (IAM) → Add role assignment.
-
Select Foundry User and assign it to the Saidot service principal.
You can switch to Option A later: assign the custom role, then remove Foundry User.
See Microsoft's Role-based access control for Microsoft Foundry.
Step 3. Enter the Foundry resource details
-
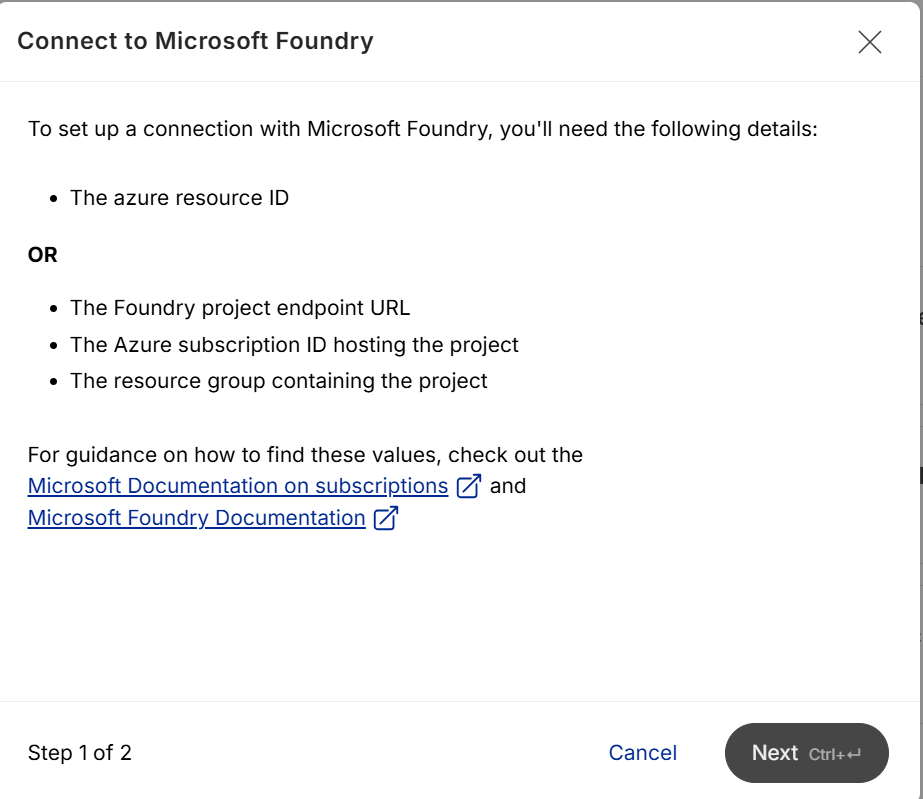
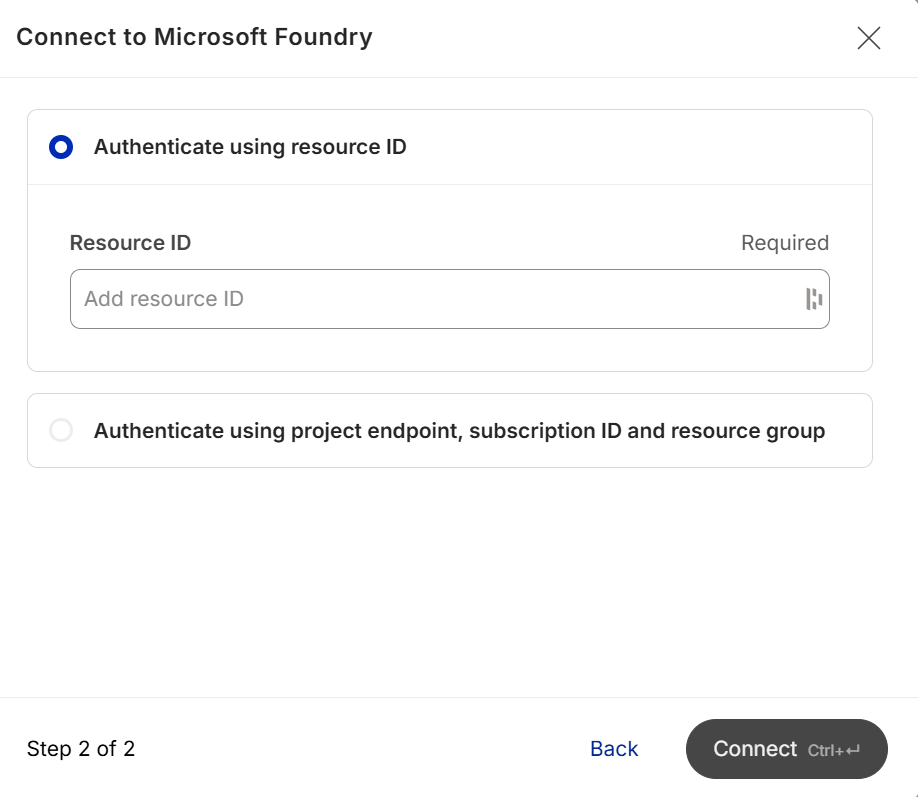
In Saidot, go to Integrations in your Space and select Connect on Microsoft Foundry.
-
The first screen lists the details you need. Select Next.
-
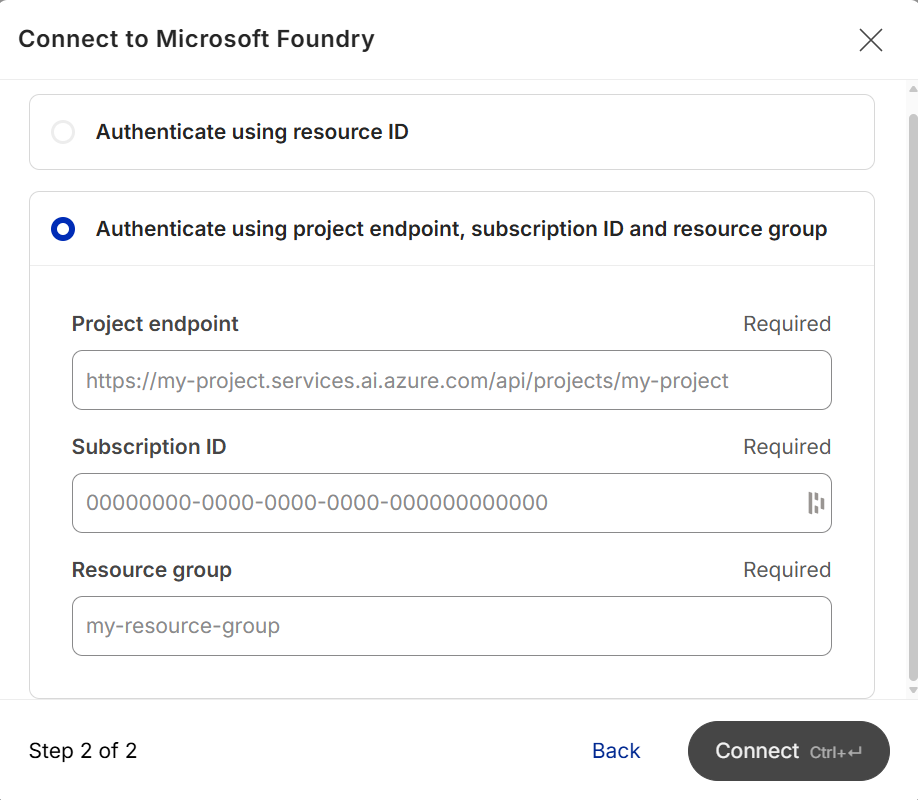
Enter one of these:
-
Option 1: the Azure resource ID of the Foundry resource.
-
Option 2: the Foundry project endpoint URL, the subscription ID hosting the project, and the resource group containing the project.
-
-
Select Connect.
Where to find the values
|
Value |
Where to find it |
Format |
|---|---|---|
|
Azure resource ID |
Azure Portal → your Foundry resource → Overview → JSON View, then copy Resource ID |
|
|
Foundry project endpoint URL |
Microsoft Foundry portal → your project → Overview (project home page), then copy Project endpoint |
|
|
Subscription ID |
Azure Portal → your Foundry resource → Overview → Subscription ID |
A GUID, for example |
|
Resource group |
Azure Portal → your Foundry resource → Overview → Resource group |
The resource group name |
Next: import models and agents – see Integrations.